Identity release assurance
Release Governance: CIAM
“Is this customer identity release secure and compliant enough to ship?”
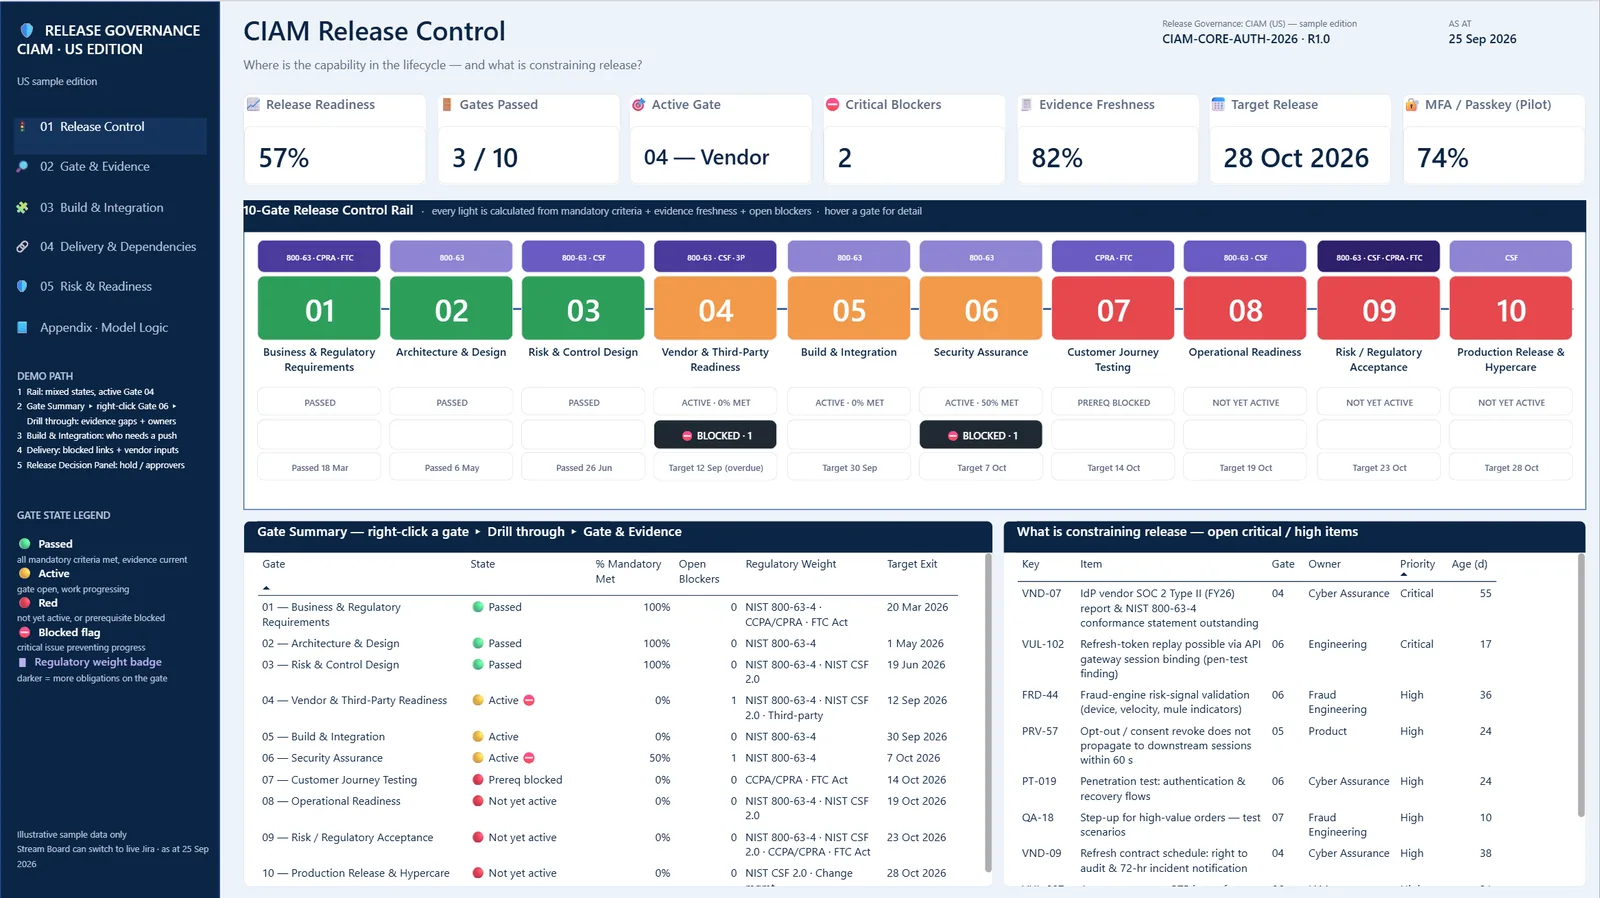
6 report pages · hover to hold, select a frame to view it
What it shows
- A 10-gate release rail, each gate tagged with the regulations it carries.
- Every gate state calculated from mandatory criteria, evidence freshness and open blockers.
- Build and integration, and delivery dependency views for engineering and vendor streams.
- What is constraining release: open critical and high items with owner and age.
Outcomes
- A defensible go / no-go decision with the evidence trail behind it.
- Blockers and vendor dependencies visible before the release date slips.
- Vendors, security and delivery working from one gate status per release.
Built for: Identity program leads, release managers and risk teams shipping customer identity changes.
Product specification
Six report pages: Release Control, Gate & Evidence, Build & Integration, Delivery & Dependencies, Risk & Readiness, and a Model Logic appendix.
A gate passes only when its mandatory criteria are met, its evidence is current and no blocker is open. Two regulatory packs: CIAM (AU) maps to CPS 234, CPS 230, the Consumer Data Right and the Privacy Act; CIAM (US) maps to NIST SP 800-63-4, NIST CSF 2.0, CCPA/CPRA, the FTC Act, OWASP ASVS and WCAG 2.2.
- Pages
- 6
- Gates
- 10, Requirements to Hypercare
- Editions
- CIAM (AU) · CIAM (US)
- Format
- Power BI (PBIP), CSV / Jira exports
How it's delivered: days, not months
- ScopeA short call to agree the decision it needs to support and which data you already have.
- LoadYour exports go into the model's CSV templates. No live connection to your systems is needed to start.
- RunThe model runs on your data, and every number traces back to its inputs and the documented method.
- Hand overYou keep the Power BI file, its design walkthrough and engineering companion, or our practitioners run it with you each month.
See Release Governance: CIAM running on your own data.